When a data breach occurs, most organizations immediately face two simultaneous obligations. The technical team moves to contain the incident. Legal moves to understand what happened and what the organization has to disclose, to whom, and by when. What most organizations discover in that moment is that their legal hold process was never designed to handle both at the same time.
The result is predictable. The technical response team remediates. Logs get overwritten. Systems get restored. And the forensic evidence that would have established what happened, when, and how, the evidence that regulators will ask for and opposing counsel will demand, has been altered or destroyed by the same response that was supposed to protect the organization.
A cybersecurity legal hold strategy is what prevents that from happening. It is not a luxury for organizations with sophisticated legal departments. It is a baseline requirement for any organization that handles sensitive data and faces potential regulatory scrutiny after a breach.
What a Cybersecurity Legal Hold Actually Covers
Most people are familiar with legal hold in the context of document-centric litigation: email, contracts, financial records. A cybersecurity legal hold covers different territory.
System logs and network activity records establish the scope and timeline of the intrusion. Without them, the organization cannot determine what data was accessed, when the breach began, or what the attackers did after they got in. These records have the shortest shelf life of any evidence in a breach scenario. Log rotation policies purge them continuously, and without a cybersecurity legal hold that suspends those routines from the first hour, they may be gone before anyone thinks to look.
Forensic images of affected systems capture the state of the environment at the time of the breach, before remediation activities alter it. Once a system is patched, restored, or reimaged, that evidence no longer exists in its original form.
Incident response communications between IT, legal, and leadership are frequently relevant in regulatory proceedings and litigation. They establish what the organization knew, when it knew it, and what decisions were made in response.
Vendor and third-party communications, particularly where the breach originated at or passed through a third-party system, are essential to establishing scope, liability, and the full timeline of the incident.
The cybersecurity legal hold obligation arises the moment the organization reasonably anticipates legal or regulatory action, which in most breach scenarios means within hours of incident discovery, not days or weeks later.
The Regulatory Clock That Will Not Wait
One of the most misunderstood aspects of cybersecurity legal hold is the relationship between the forensic investigation and the regulatory notification timeline. Organizations often assume they need to understand the breach before they can notify regulators. The regulatory clock operates differently.
GDPR requires notification to the relevant supervisory authority within 72 hours of discovering a breach. The SEC requires disclosure within four business days of determining a breach is material. HIPAA allows 60 days from discovery for breach notification.
None of these clocks wait for the forensic investigation to be complete. They run from discovery or determination, regardless of whether the organization has a full picture of what happened. The evidence needed to accurately assess scope, meet notification obligations, and defend the organization’s response in subsequent legal proceedings needs to exist and be preserved before those deadlines expire.
An organization that remediates first and preserves second may find itself unable to demonstrate to regulators exactly what data was accessed, which affected individuals need to be notified, or what the scope of the incident actually was. That is not a forensic problem at that point. It is a legal hold data preservation failure.
Where Most Legal Hold Processes Fail in a Cybersecurity Context
The Containment Versus Preservation Conflict
Technical response teams are trained and incentivized to contain and remediate as quickly as possible. That is the right instinct for stopping the damage. It is directly in conflict with legal hold data preservation, which requires that relevant evidence not be altered or destroyed.
Without a cybersecurity legal hold protocol that runs alongside the technical response rather than after it, these two objectives compete. Containment typically wins because it is urgent, visible, and has an obvious success metric. Preservation loses because it is invisible, its failure only surfaces later, and nobody gets credit for the evidence that was not destroyed.
The Scope Problem
Standard legal hold processes are designed around known custodians and document sets. The relevant evidence in a cybersecurity matter is not a document set. It is network logs, endpoint forensic images, SIEM data, firewall records, and cloud service activity spanning systems that most document-centric legal hold processes were never designed to reach.
LHP legal hold software and comparable platforms are highly effective for managing document-centric legal hold data preservation. In a cybersecurity context, they may need to be supplemented with forensic preservation capabilities that operate at the system level rather than through custodian notice and compliance.
The Timing Problem
Volatile data, including active memory, running processes, and session-level network connections, disappears within seconds to minutes of a system being powered down or restarted. A cybersecurity legal hold that issues notices and waits for acknowledgement will miss this evidence entirely. System-level preservation has to be triggered immediately, not after a custodian reads and responds to a notice.
The Documentation Problem
Regulators and courts evaluating an organization’s breach response will examine not just what was preserved, but when the decision to preserve was made, what triggered it, and what methodology governed it. An organization that cannot produce a timestamped, documented legal hold data preservation record for its breach response is in a significantly weaker position than one that can demonstrate the preservation decision was made at the right moment and executed correctly.
What a Cybersecurity-Ready Legal Hold Strategy Looks Like
Pre-Incident Integration
The cybersecurity legal hold protocol needs to be part of the incident response plan before an incident occurs. Legal, IT, and compliance need to agree on the triggering conditions for legal hold data preservation in advance, so the decision does not have to be made under pressure in the middle of an active breach.
This means defining, before anything happens, which data sources trigger automatic preservation, who has authority to issue the hold, what the first preservation steps are, and how technical containment and legal hold data preservation run simultaneously rather than sequentially.
Preservation That Runs Alongside Containment
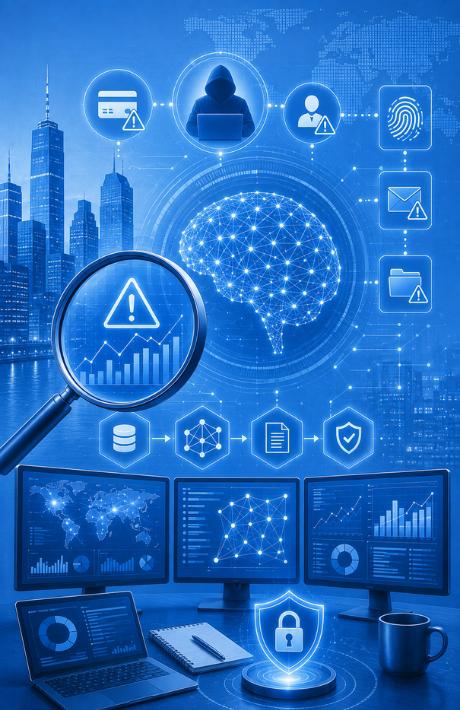
Platform-level preservation of relevant log data, forensic images, and communications needs to begin at the same time as technical containment, not after the immediate threat has been addressed. This requires a legal hold capability that operates at the system level, integrated into the incident response workflow rather than added as an afterthought once the technical work is done.
Platform Coverage Built for Cybersecurity Evidence
A cybersecurity legal hold needs to reach the data sources where breach evidence lives: SIEM platforms, endpoint detection and response systems, cloud service logs, network flow data, and forensic images of affected systems. Organizations evaluating LHP legal hold software, Legal Hold Pro alternatives, or comparable platforms for their cybersecurity matters should assess whether those platforms can reach technical data sources, not just document custodians.
A Documented Audit Trail From the First Hour
Every legal hold data preservation decision made during a breach response should be timestamped, logged, and tied to the preservation framework governing the matter. That record is what the organization produces when regulators ask how it managed its preservation obligations, and what courts examine when spoliation is alleged.
Where Specialized Expertise Changes the Outcome
Organizations that have integrated their cybersecurity legal hold and incident response programs manage regulatory scrutiny significantly better than those that treat them as separate functions.
The forensic team handling the technical investigation and the legal hold team managing preservation need to operate from the same factual record from the first hour of the incident. When they do, the evidence is there when regulators ask for it. When they do not, the question of what happened becomes harder to answer precisely when the stakes of answering it correctly are highest.
A cybersecurity legal hold strategy is not a document that gets drafted after a breach occurs. It is infrastructure that gets built before one does. The window for preserving the right evidence in a breach scenario is measured in hours. Organizations that build the protocol before they need it are the ones positioned to execute it correctly when they do.
Legal hold data preservation in a cybersecurity context requires the same rigor, the same documentation, and the same auditable methodology as any other legal hold engagement. The only difference is the data sources, the timeline, and the consequences of getting it wrong.
Gemean integrates cybersecurity legal hold protocols into its breach response and digital forensics engagements, ensuring that legal hold data preservation and technical investigation proceed together from the first hour of an incident.
What is a cybersecurity legal hold and when does it apply?
A cybersecurity legal hold is a preservation obligation that arises when an organization anticipates legal or regulatory action following a cybersecurity incident. It applies from the moment the organization discovers or reasonably suspects that a breach may lead to litigation, a regulatory inquiry, or an enforcement proceeding, which in most scenarios means immediately upon discovering the incident.
What data needs to be preserved after a data breach?
Legal hold data preservation in a breach context covers system logs and network activity records, forensic images of affected systems, incident response communications, email and collaboration platform records related to the incident, and vendor or third-party communications where relevant. The specific scope depends on the nature of the breach and the regulatory frameworks that apply.
What is the difference between incident response and legal hold data preservation?
Incident response is focused on containing and remediating the breach. Legal hold data preservation is focused on protecting evidence of what happened before remediation activities alter it. The two objectives are in direct conflict unless a cybersecurity legal hold protocol is designed to run alongside incident response rather than after it.
How does LHP legal hold software support cybersecurity matters?
LHP legal hold software and comparable platforms are highly effective for document-centric legal hold data preservation, including custodian notice management, acknowledgement tracking, and auditable matter records. In a cybersecurity context, they may need to be supplemented with forensic preservation capabilities that operate at the system level to capture technical evidence that document-centric platforms were not designed to reach.
What are the regulatory notification timelines that affect legal hold strategy after a breach?
GDPR requires notification within 72 hours of discovering a breach. The SEC requires disclosure within four business days of determining a breach is material. HIPAA allows 60 days from discovery. None of these timelines wait for the forensic investigation to conclude, which is why legal hold data preservation needs to begin simultaneously with incident response rather than after the technical picture is clear.